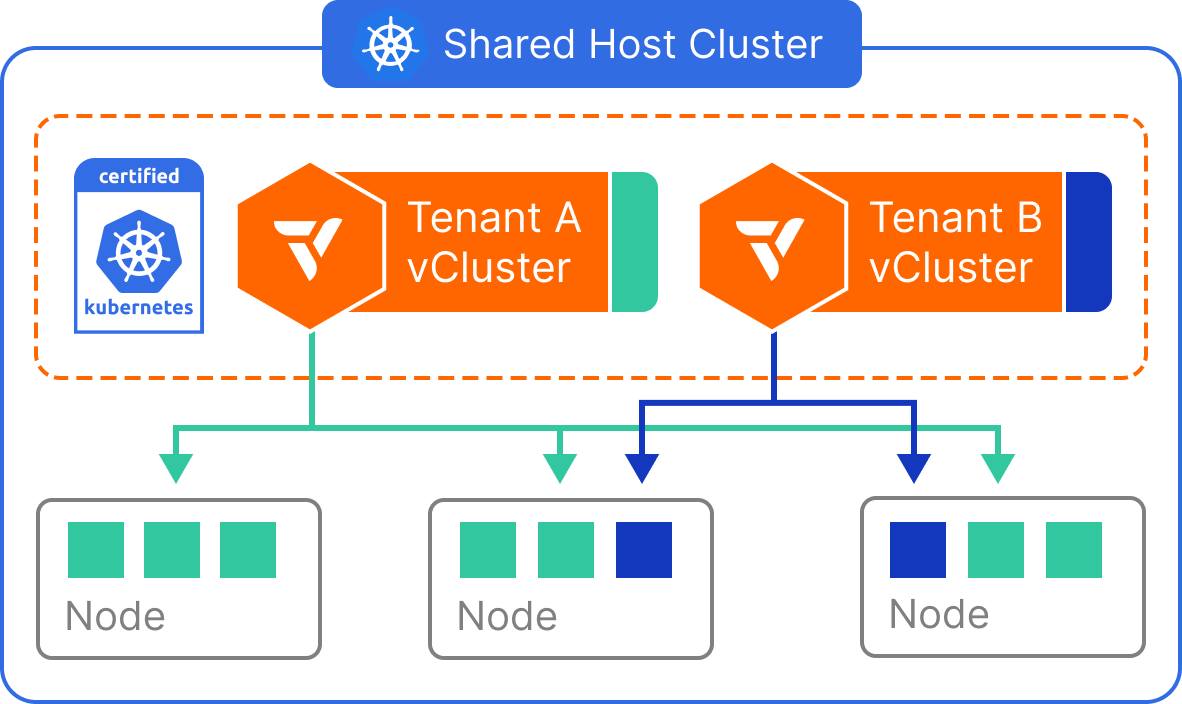
vCluster is a Kubernetes virtualization platform designed to create fully functional virtual clusters within existing namespaces. This tool allows users to run multiple isolated Kubernetes environments on a single host cluster, enhancing multi-tenancy and isolation while reducing costs compared to separate full clusters.
Key Features:
Isolation and Multi-Tenancy: Each vCluster operates in its own namespace, providing strong isolation for enhanced security and resource management.
Cost-Effective: Reduces infrastructure expenses by utilizing shared resources instead of dedicated clusters.
Security and Isolation: Offers granular permissions and an isolated control plane, minimizing risks associated with privileged access.
Flexibility in Environments and Storage: Supports various Kubernetes versions and distributions, along with adaptable backing stores like SQLite or etcd for scalability needs.
Scalability Enhancements: Reduces API server load through independent management of CRDs within each cluster.
Audience & Benefit:
Ideal for platform engineers, DevOps teams, cloud providers, and organizations requiring scalable Kubernetes solutions without high infrastructure costs. vCluster enables secure, efficient multi-tenant deployments, allowing teams to manage resources independently with reduced complexity and overhead.
This tool is installed via winget, offering a seamless setup process.
README
Tenant Clusters for AI clouds, AI factories, and production Kubernetes
Run your infrastructure like a hyperscaler. Every team, customer, and training run gets its own isolated cluster.
CNCF Certified Kubernetes · Distribution · Kubernetes AI Conformant
About
vCluster creates Tenant Clusters: fully isolated environments delivered as managed Kubernetes, or as the foundation for Slurm, Ray, Run:ai and inference clusters. Each gets its own API server, CRDs and RBAC, and runs on an existing cluster or standalone on bare metal. CNCF Certified Kubernetes.
Every cluster becomes a product you can ship. Sell it to customers or serve it to internal teams from the same platform, with each tenant seeing only their own cluster and nothing else. The control plane stays invisible to tenants: no shared control plane nodes, no in-cluster agent pods, and no lateral path between environments.
Because a Tenant Cluster is upstream Kubernetes, everything built for the standard API works against it unmodified: kubectl, Helm, Argo, Crossplane, operators, and CRDs.
40M+ Tenant Clusters deployed. vCluster runs in production at Adobe, CoreWeave, NVIDIA, Nebius, Lintasarta, Atlan, Deloitte, and across 50+ AI clouds and Fortune 500 platform organizations, powering 100K+ GPUs and 1M+ CPUs.
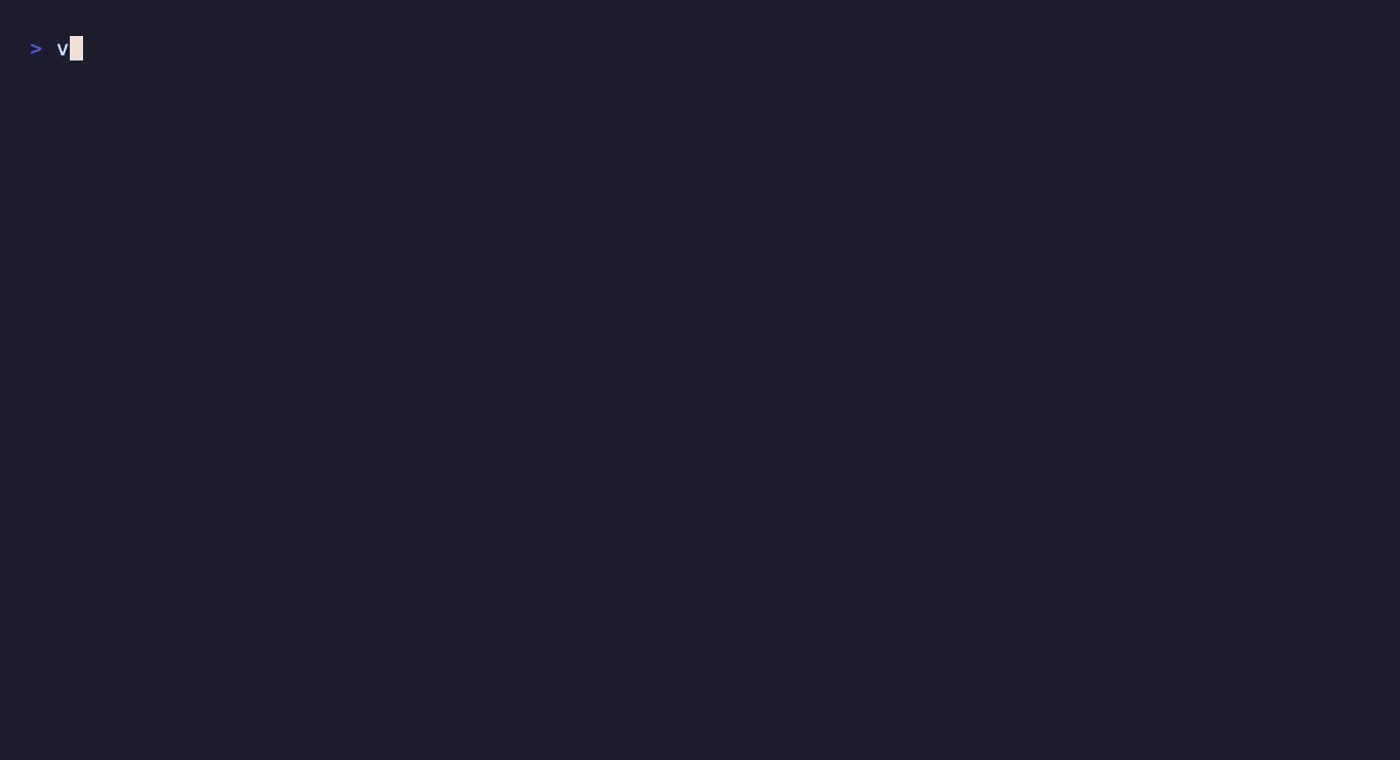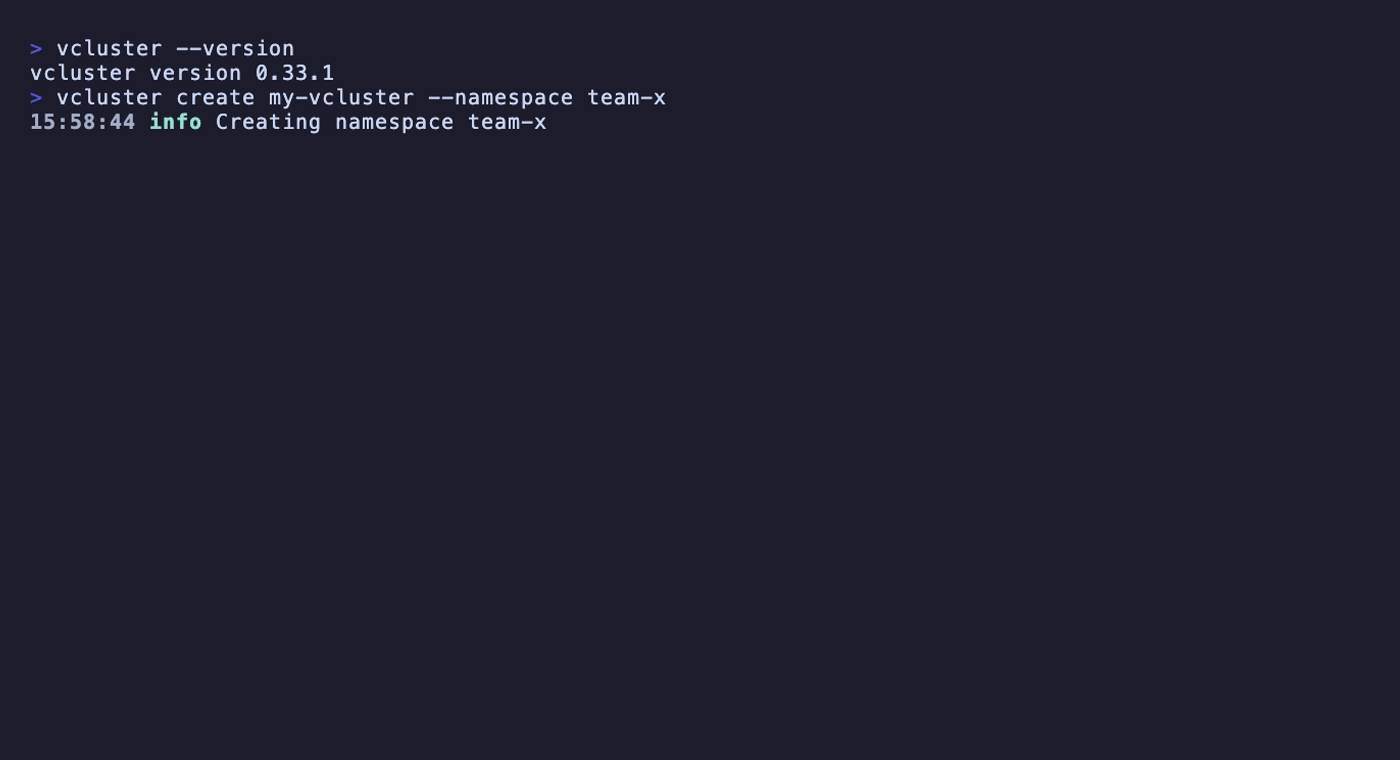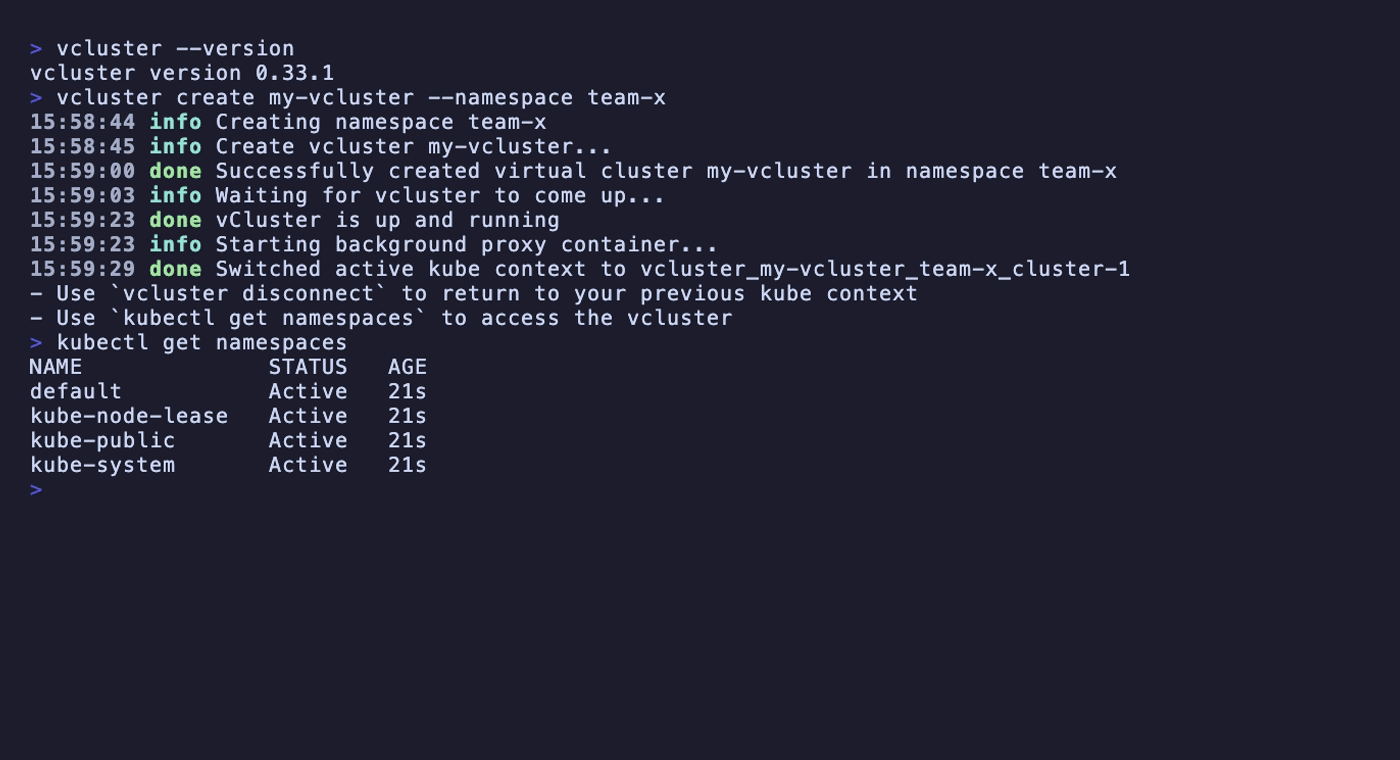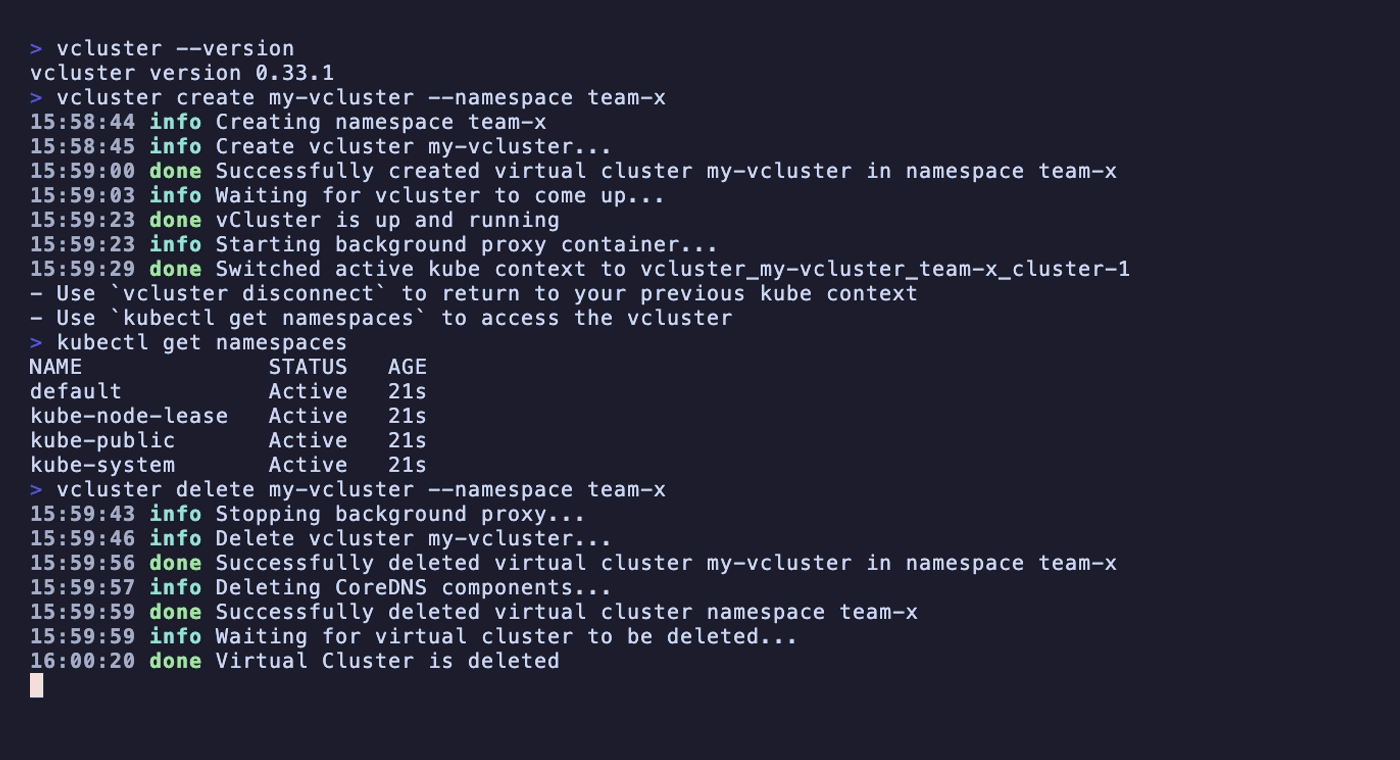
🚀 Quick start
# Install the vCluster CLI
brew install loft-sh/tap/vcluster

# Create a Tenant Cluster
vcluster create my-vcluster --namespace team-x

# Use kubectl as usual. You are now inside your Tenant Cluster.
kubectl get namespaces
Prerequisites: a running Kubernetes cluster and kubectl configured.
No Kubernetes cluster? Run a complete Tenant Cluster in Docker containers with vind (vCluster in Docker). Like kind, but with the full vCluster feature set: UI, sleep and resume, LoadBalancer, image cache, and external nodes joining over VPN.
vcluster create my-vcluster --driver docker
kubectl get namespaces
🎮 Try it in the browser
🎁 vCluster free tier
Real usage, not a gated demo. Unlimited Tenant Clusters up to 64 CPUs and 32 GPUs, plus the full vCluster Platform UI, for free. Get started free →
🧩 Every kind of cluster
One platform turns raw compute into the cluster type each tenant actually asks for. Kubernetes is the foundation; the rest are delivered on top of it.
Cluster type
What a tenant gets
Kubernetes Clusters
A dedicated, CNCF-certified Kubernetes cluster with its own API server, CRDs, and RBAC
Nested Clusters
Tenant Clusters running on the Control Plane Cluster's shared nodes for maximum density
Inference Clusters
Serving stacks such as Dynamo and llm-d, isolated per tenant
Ray Clusters
Ray for distributed training and data processing, isolated per tenant
Run:ai Clusters
Run:ai scheduling on top of an isolated Tenant Cluster
Slurm Clusters(Beta)
Managed Slurm for HPC and batch training
Agent Sandbox Clusters(Coming soon)
Isolated clusters for agentic and untrusted code execution
Slurm, Ray, Run:ai, inference, and agent sandbox clusters are delivered through vCluster Platform. This repository is the open-source engine that every one of them is built on.
vCluster supports multiple deployment architectures. Two things vary independently: where the control plane runs (an existing Kubernetes cluster, a standalone binary, or Docker) and how tenant workloads are placed (shared nodes or private nodes). The modes below combine them, offering progressively stronger isolation from dense shared infrastructure through to fully standalone deployments on bare metal.
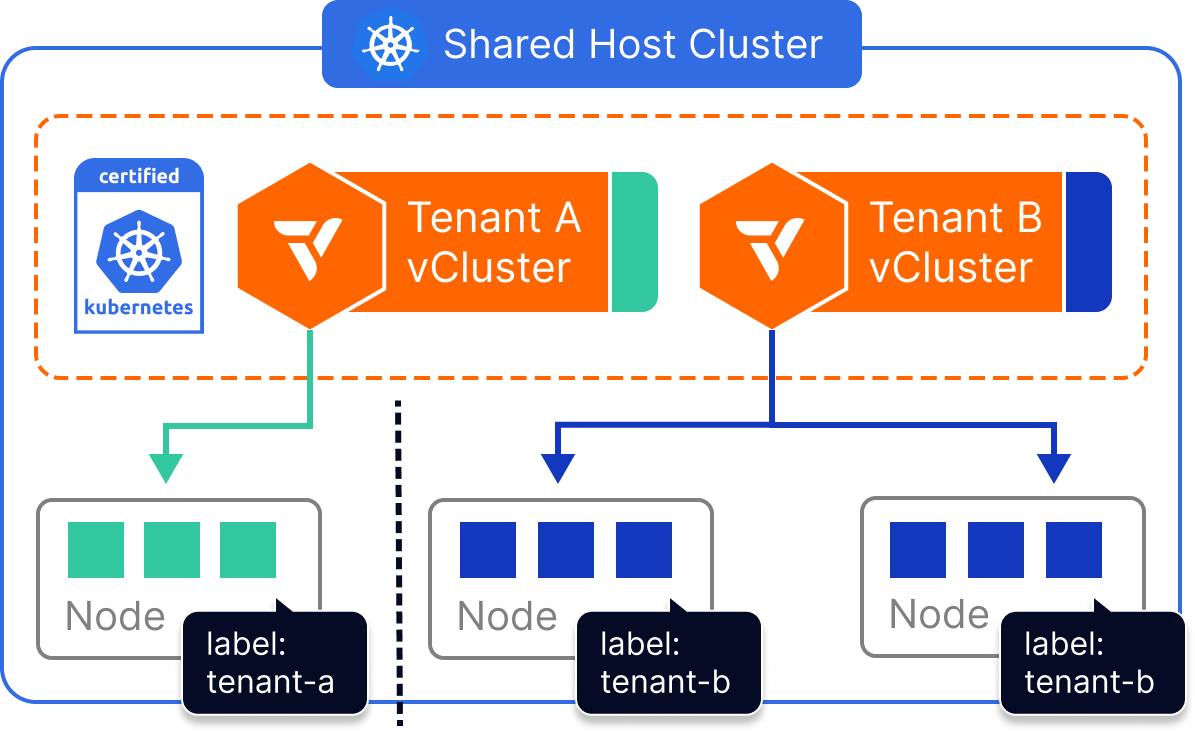
🔹 Dedicated Nodes: isolated compute on labeled node pools
Tenant Clusters get their own set of labeled nodes on the Control Plane Cluster. Workloads are isolated but still managed by the Control Plane Cluster.
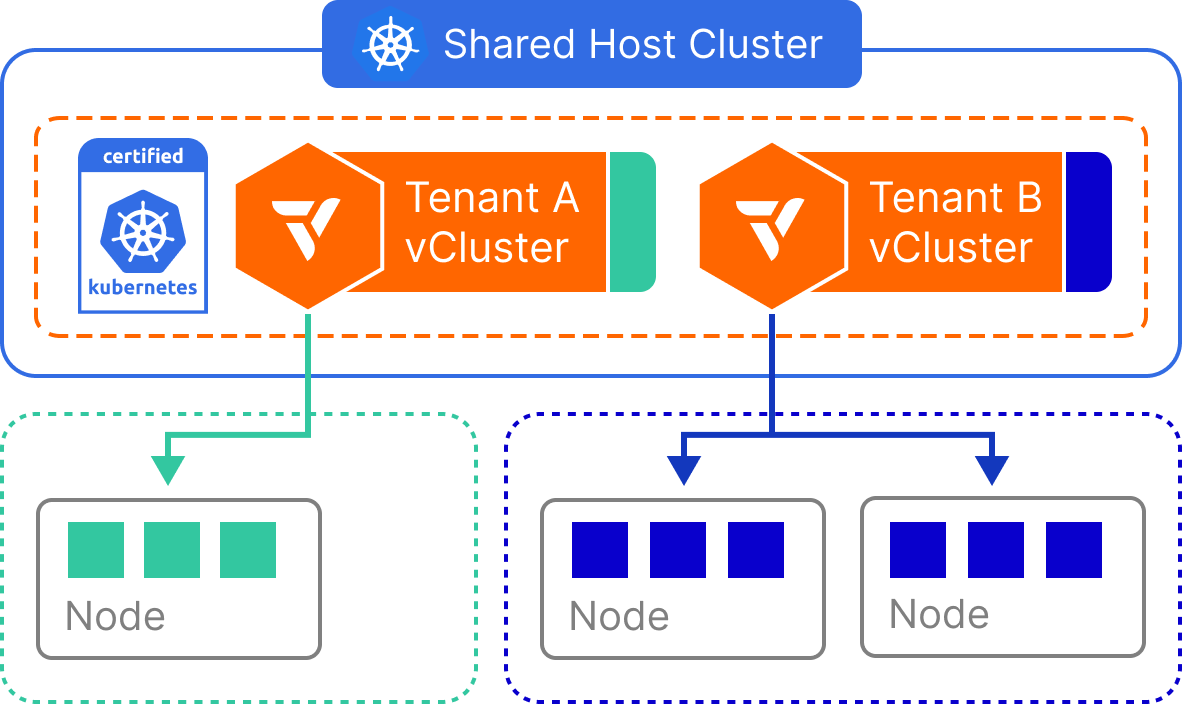
🔹 Private Nodes v0.27+: full CNI/CSI isolation
External nodes join the Tenant Cluster directly with their own CNI, CSI, and networking stack, through a token-based process. No cross-tenant visibility, and complete infrastructure separation from the Control Plane Cluster. Nodes can also join over an encrypted VPN overlay v0.30+, so one Tenant Cluster can span sites, networks, and clouds.
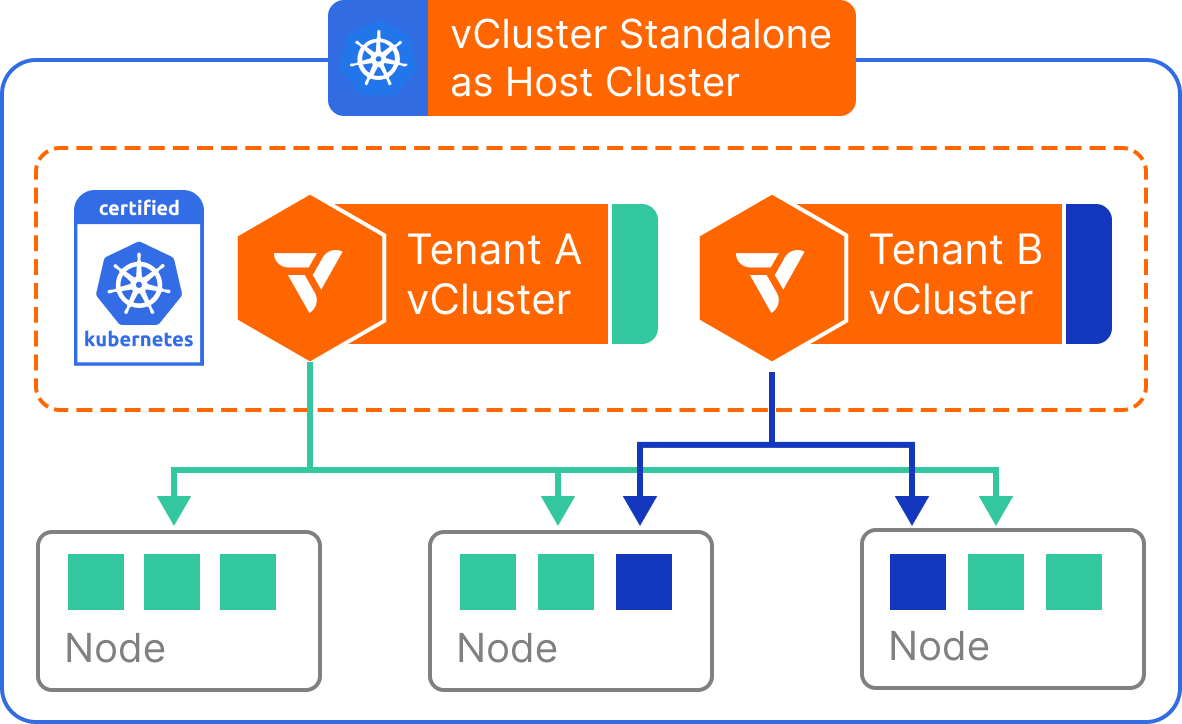
🔹 vCluster Standalone v0.29+: no Control Plane Cluster required
A complete, zero-dependency Kubernetes distribution. Run the whole control plane as a self-contained binary directly on bare metal or VMs. This is how providers solve the "cluster one" problem when building infrastructure from scratch.
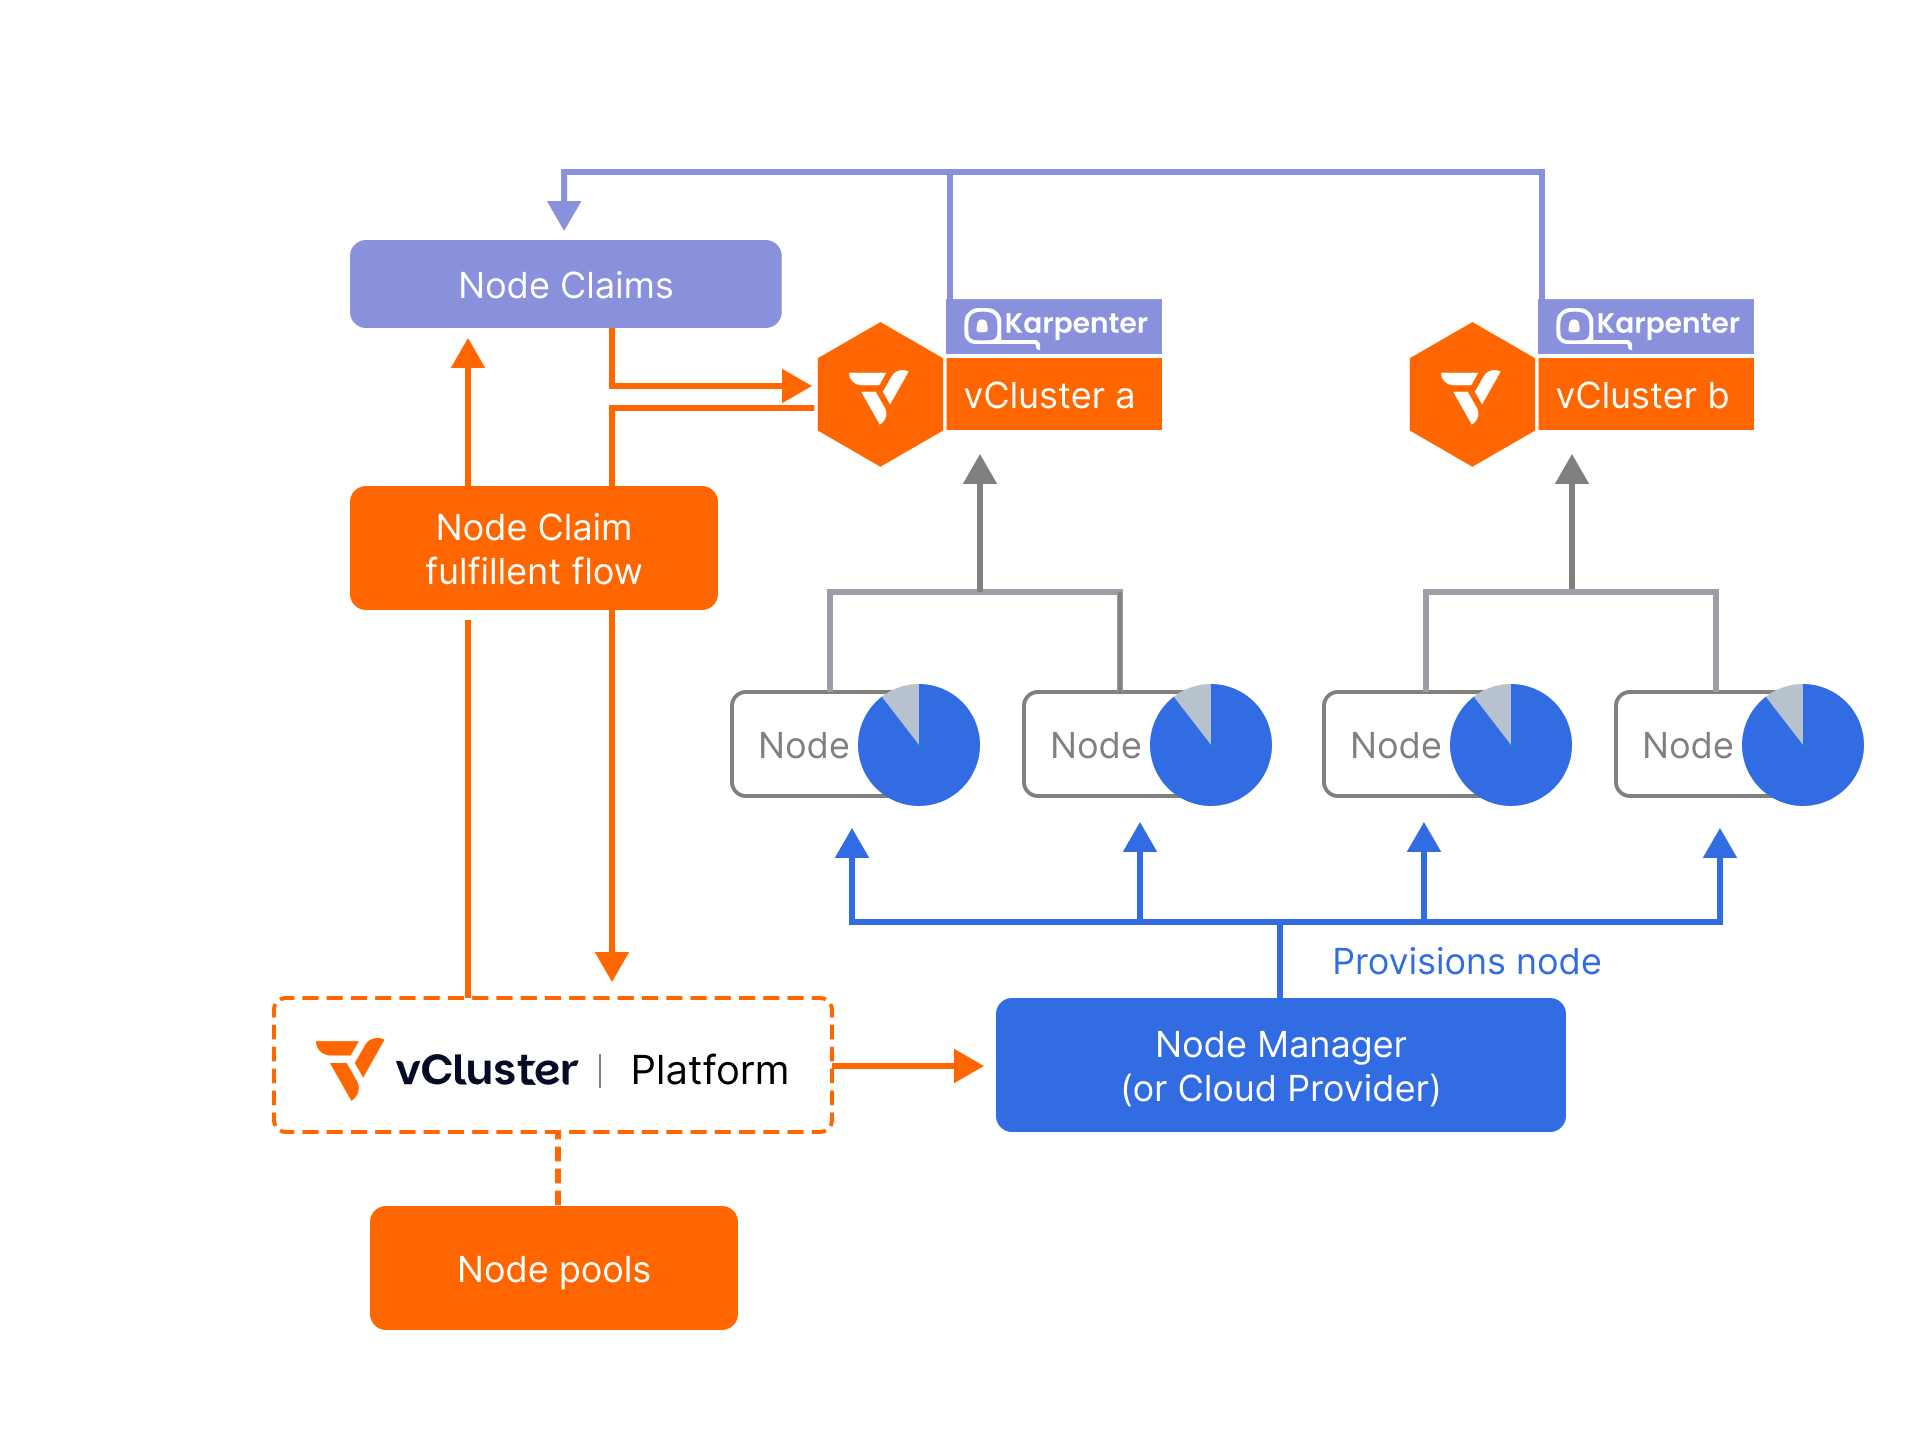
⚡ Auto Nodes v0.28+: Karpenter-powered dynamic autoscaling
Automatically provision and deprovision private nodes based on workload demand. Works across public cloud, private cloud, hybrid, and bare metal environments. Node profiles v0.36+ let each pool carry its own node configuration.
🐳 vind v0.32+: a complete Tenant Cluster in Docker, no Kubernetes required
The control plane and worker nodes run as containers on a single Docker host, using private nodes underneath. There is no Control Plane Cluster and no Kubernetes dependency at all, which makes this the fastest way to get a real Tenant Cluster on a laptop or a CI runner. Docker deployment is driven by the CLI rather than by vcluster.yaml.
vcluster create my-vcluster --driver docker
✨ Key features
Feature
Description
🎛️ Its own API server, per tenant
Every Tenant Cluster runs a dedicated control plane: API server, controller manager, and data store. Full Kubernetes API isolation, not a namespace with rules layered on top
🔒 Strong tenant isolation
Tenants hold admin inside their Tenant Cluster while holding minimal permissions on the Control Plane Cluster
🎮 GPU-aware scheduling
Dynamic Resource Allocation with resource claims, resource claim templates, and device classes, plus in-place pod resizing
⚡ Auto Nodes
Karpenter-powered provisioning and deprovisioning of private nodes across cloud, hybrid, and bare metal, with per-pool node profiles
🖥️ Standalone deployment
Run without a Control Plane Cluster on dedicated infrastructure or bare metal, purpose-built for AI factories and on-prem GPU fleets
🐳 Runs on Docker
A complete Tenant Cluster in Docker containers with no Kubernetes dependency, through vcluster create --driver docker
🔐 Node VPN(Platform)
Private nodes join over an encrypted overlay, so a single Tenant Cluster can span sites, networks, and clouds
📸 Snapshot and restore
Snapshot a Tenant Cluster to S3, OCI, Azure Blob, or local storage, and restore it elsewhere
💤 Sleep mode(Platform)
Pause inactive Tenant Clusters to save resources, with instant wake when needed
🔗 Shared platform stack(Shared / Dedicated Nodes)
Reuse the Control Plane Cluster's CNI, CSI, ingress, and other infrastructure, with no duplicate platform components
🔄 Resource syncing(Shared / Dedicated Nodes)
Bidirectional sync of any Kubernetes resource: pods, services, secrets, configmaps, CRDs, and Gateway API objects
🧩 Integrations
Native support for cert-manager, external-secrets, KubeVirt, Istio, and metrics-server
📊 High availability
Multiple replicas with leader election. Embedded etcd or external databases (PostgreSQL, MySQL, RDS)
> Shared platform stack, resource syncing, and Control Plane Cluster integrations apply in Shared and Dedicated Nodes modes, where the Tenant Cluster reuses the Control Plane Cluster's CNI, CSI, and platform stack. Private Nodes and Standalone deployments bring their own CNI, CSI, and platform components.
Start turnkey with the vCluster Platform UI and CLI, or call the APIs and put your own portal and brand in front. It is a two-way door, with no re-platforming.
🌐 The vCluster stack
vCluster is the foundation of a broader platform for running Kubernetes and AI infrastructure on your own hardware, from a single rack to 100K-GPU superclusters.
Hardware-enforced network isolation via programmatic VLANs, VRFs, and ACLs
Together they provide the full stack for an AI factory: certified Kubernetes, isolated Tenant Clusters, runtime workload sandboxing, and GPU infrastructure operations. The ClusterMAX™ security criteria call for strong isolation between tenants, and name vNode Private Nodes.
🏢 Trusted by
NebiusAI cloud tenant isolation
QumulusAI1 min to spin up isolated K8s
Polarise100% data residency at the infra layer